01The premise
Different from another scanner
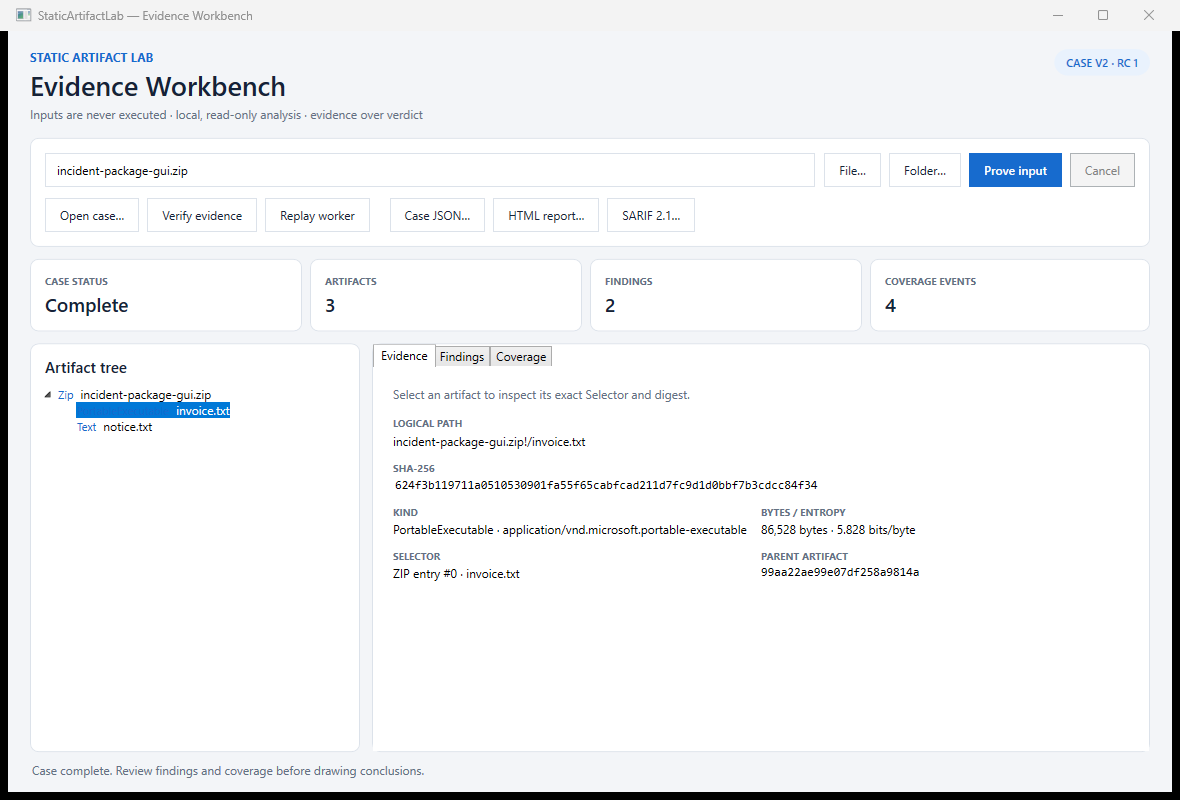
StaticArtifactLab does not decide whether a file is malware. It builds a reproducible inventory. A root file is bound to path, length and SHA-256. A ZIP child also receives parent ID and digest, normalized entry name, entry index, length and its own digest.
This canonical combination creates a short artifact ID for stable references while the full SHA-256 remains the content digest. ZIP, JAR, NuGet, APK and OOXML packages use the same bounded container path.
02Inside the system
Nested artifacts with proof of provenance
prove
Inventories a file or directory, recursive ZIP-compatible containers, findings and coverage in Case v2.
INVENTORY / CASE V2verify
Recomputes canonical IDs and parent relations without reading a path merely because the case names it.
STRUCTURE FIRSTverify --with-sources
Explicitly reopens available local ZIP entries and checks index, name, length and SHA-256. UNC paths remain blocked.
SOURCE CHECKreplay
Runs the named worker with stored limits and separates added, removed and changed evidence paths.
DETERMINISTIC DIFFCoverage and limits
Nine stored limits expose skipped or rejected work and mark the case partial when required.
SKIPPED / REJECTEDReports
Case v2 JSON, standalone HTML with a restrictive CSP, and SARIF 2.1 bind the same rules and artifact paths.
JSON / HTML / SARIF03Concrete workflow
Limits are part of the result
Root and child size, expanded byte budget, artifact count, filesystem nodes, ZIP entries, depth, expansion ratio and finding count are stored in the case. Hitting a limit emits skipped or rejected coverage. An empty result therefore cannot look like a complete analysis.
static-artifact.exe prove .\incoming\package.zip --out .\evidence\package.sal-case.json
static-artifact.exe verify .\evidence\package.sal-case.json --with-sources
static-artifact.exe replay .\evidence\package.sal-case.json
From input to evidence
Prove
Root and accepted children bind to selector, length and digest.
Cover
Analyzed, skipped and rejected work remains visible.
Verify
Structure and optionally available source bytes are checked again.
Replay
The stored worker and limit contract runs reproducibly.
Design boundaries
What provenance means here—and what it does not
- Not antivirus, a sandbox or forensic chain of custody
- Does not sign the case or prove the original origin of a file
- Executes nothing, loads no inspected assembly and contacts no network service
- Does not follow symlinks or reparse points
- Absolute or parent-traversing archive paths are reported but never accepted as children
05RC facts
StaticArtifactLab · RC facts
- Release candidate
- 1.0.0-rc.1
- Workflows
- prove, verify, replay
- Recursive containers
- ZIP, JAR, NuGet, APK and OOXML
- Evidence
- parent, selector, length, SHA-256, format, entropy and coverage
- Exports
- Case v2 JSON, standalone HTML, SARIF 2.1
- Interfaces
- Windows WPF and Windows/Linux CLI
- Quality assurance
- 51 automated tests in the RC state
- Safety boundary
- read-only, no execution, no network, no extraction to disk
These bytes were actually inspected through this path under these limits.